- 홈페이지 /
- 서적 /
- Computing & Internet /
- Networking & Security /
- Introduction to Network & Security /
- Practical Detection Engineering with Sigma: I...
0 ratings




제품번호 #:
267526897
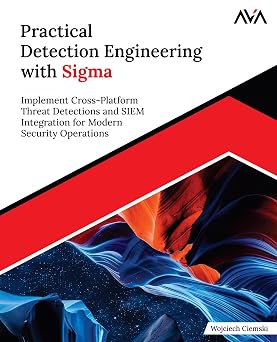
Practical Detection Engineering with Sigma: Implement Cross-Platform Threat Detections and SIEM Integration for Modern Security Operations (English
제품번호 #:
267526897
KRW 92913
Price Details
Excluding Shipping & Custom charges ( Shipping and custom charges will be calculated on checkout )
*All items will import from 영국
0 ratings
리뷰 작성
재고
 UK 스토어에서 가져옴
QTY:
지금 주문하시면 도착 예정일 Monday, 10월 19
Secured transaction
Ubuy works hard to protect your security and privacy. Our advanced payment security system ensures confidentiality by encrypting your information during transmission using AES (Advanced Encryption Standards) and SSL (Secure Socket Layer) protocols. Your payment details are 100% secure as we do not share your payment details with third party sellers.
Our Top Logistics Partners


Fast
Shipping

Free
Return*

Secure Packaging

100% Original Products

PCI DSS Compliance

ISO 27001 Certified



제품 세부 정보
- Write Once, and Detect Everywhere- Practical Sigma Rules for Modern SOCsKey Features● Get a free one-month digital subscription to www.avaskillshelf.com● End-to-end guide to writing, testing, and deploying Sigma detection rules across Windows, Linux, and network log sources.● Step-by-step conversion of Sigma rules into backend-specific queries for Elastic, Splunk, Microsoft Sentinel, and Wazuh.● Practical detection-as-code approach including version control, CI/CD pipelines, rule lifecycle management, and production-ready workflows.Book DescriptionPractical Detection Engineering with Sigma is a hands-on guide to building, testing, and operationalizing modern detections in real SOC environments.The book walks you step by step through the full detection engineering lifecycle—from understanding Sigma fundamentals to writing structured rules and deploying them across SIEM and XDR platforms.You will learn how to translate adversary behavior into behavior-based detections, aligned with MITRE ATT&CK, create rules for Windows, Linux, and network telemetry, and convert them into backend-specific queries for platforms such as Elastic, Splunk, Microsoft Sentinel, and Wazuh. Practical examples demonstrate how to validate detections using real and simulated attack data, reduce false positives, and design alerts that analysts can confidently triage.From rule creation to CI/CD automation, version control, and large-scale rule management, this book equips you to build scalable, maintainable, and production-ready detection programs aligned with modern security operations.What you will learn● Design and write structured, maintainable Sigma rules for diverse log sources and enterprise environments.● Translate adversary techniques into behavior-based detections, aligned with MITRE ATT&CK tactics and techniques.● Convert vendor-agnostic Sigma rules into optimized SIEM and XDR platform-specific queries.● Validate and test detections using real telemetry, simulated attacks, and threat emulation frameworks.● Reduce false positives through better logic design, field normalization, and contextual enrichment.● Implement scalable detection engineering practices using Git-based versioning, automation, and CI/CD pipelines.Table of Contents1. Understanding Sigma and Its Importance2. Anatomy of a Sigma Rule3. Sigma Rule Logic and Conditions4. Creating Rules for Windows Logs5. Creating Rules for Linux and Network Logs6. ATT&CK Mapping and TTP-Based Detection7. Threat Simulation and Rule Testing8. Sigma Rule Anti-Patterns and Best Practices9. Real-World Detection Use Cases10. Sigma Rules in SOC Workflows11. Converting Sigma to SIEM Queries12. Backend Limitations and Field Mapping Challenges13. Automating Detection Delivery with CI/CD14. Managing Rule Packs and Rule Versioning15. Threat Hunting with Sigma16. Intelligence-Driven Detection Engineering17. Sigma in Open Source XDR18. The Future of Sigma and Detection-as-Code Appendices Index
| Publisher | Orange Education Pvt Ltd |
| Publication date | 26 May 2026 |
| Language | English |
| Print length | 448 pages |
| ISBN-10 | 9349887975 |
| ISBN-13 | 978-9349887978 |
| Item weight | 767 g |
| Dimensions | 19.05 x 2.57 x 23.5 cm |
제품 설명
질문이 있으십니까? 채팅하기
고객 질문 및 답변
-
의문:
Ubuy에서 온라인으로 Practical Detection Engineering with Sigma: 쇼핑하는 방법?
답변: Ubuy에서 온라인으로 Practical Detection Engineering with Sigma:을(를) 쉽게 쇼핑할 수 있습니다.. 제품을 검색하고 체크아웃하는 동안 배송 방법을 선택하고 해당 위치로 배송받기만 하면 됩니다. -
의문:
Practical Detection Engineering with Sigma:는 South Korea에서 온라인 쇼핑이 가능합니까?
답변: 예, Ubuy South Korea에서 이 제품을 합리적인 가격에 구매할 수 있습니다.. Practical Detection Engineering with Sigma:은(는) 현지에서 구할 수 없지만 특급 배송 서비스로 저희를 신뢰할 수 있습니다. -
의문:
주문 후 제품을 받는 데 얼마나 걸립니까?
답변: 주문한 제품의 배송 시간은 주문한 항목과 선택한 배송 방법에 따라 다릅니다.. 예상 배송 시간은 결제 과정에서 언급되므로 안심하고 쇼핑하십시오.
Introduction to Network & Security Editorial Review
편집 리뷰가 없습니다.
Customer Reviews & Ratings
1 고객 평가
-
5 점
100%
-
4 점
0%
-
3 점
0%
-
2 점
0%
-
1 점
0%
이 제품 리뷰하기
다른 고객들과 의견을 공유하세요.
Product Price History
중요 정보
- 제한 사항: 국제 배송되는 제품의 경우 제조업체 보증이 유효하지 않을 수 있으며, 제조업체 서비스 옵션을 사용하지 못하거나 제품 설명서, 지침 및 안전 경고가 대상 국가 언어로 표시되지 않을 수 있으며, 제품(및 첨부 자료)은 도착 국가 표준, 사양 및 라벨링 요구 사항에 따라 설계되지 않을 수 있으며, 제품은 목적지 국가 전압 및 기타 전기 표준을 준수하지 않을 수 있습니다(가능한 경우 어댑터 또는 변환기 사용 필요). 수령인은 제품을 도착 국가로 합법적으로 수입할 수 있는지 확인할 책임이 있습니다. Ubuy 또는 그 제휴사에서 주문할 때, 수령인은 기록 수입자로서 도착 국가의 모든 법률과 규정을 준수해야 합니다.
- Ubuy는 글로벌 검색 엔진이므로 Ubuy에 나열된 모든 제품이 판매용은 아닙니다. 제품은 수출/무역 규정을 따릅니다.
KRW 92913
지금 주문하시면 도착 예정일 Monday, 10월 19
This item is not restrict in my country.(Please click on above link if this item is not restrict in your country, So our team will review and allow.)
QTY:
Secured transaction
PCI DSS compliant and ISO 27001:2022 certified, with encrypted payments and full buyer protection on every order.
Our Top Logistics Partners
Fastest cross-border delivery
Ubuy Assurance
Experience worry-free shopping with 100% original products, PCI DSS-compliant payment security, ISO 27001-certified data protection, the fastest cross-border delivery, free returns *, and secure packaging on every order.